 Procura
Problem & approach
Employees need to submit purchasing needs, managers need to decide them, and reviewers need an attributed history. Administrative access should not automatically mean approval authority.
I implemented the request-to-decision slice: multi-line drafts, submission, manager approval or rejection, scoped search and persisted history. The wider procurement workspace is a roadmap, not a completed receiving or inventory system.
- 01
Draft
The owner creates and edits request lines.
- 02
Submit
Validation and a version check protect the transition.
- 03
Review
A manager decides; the decision and event commit together.
Inside the application
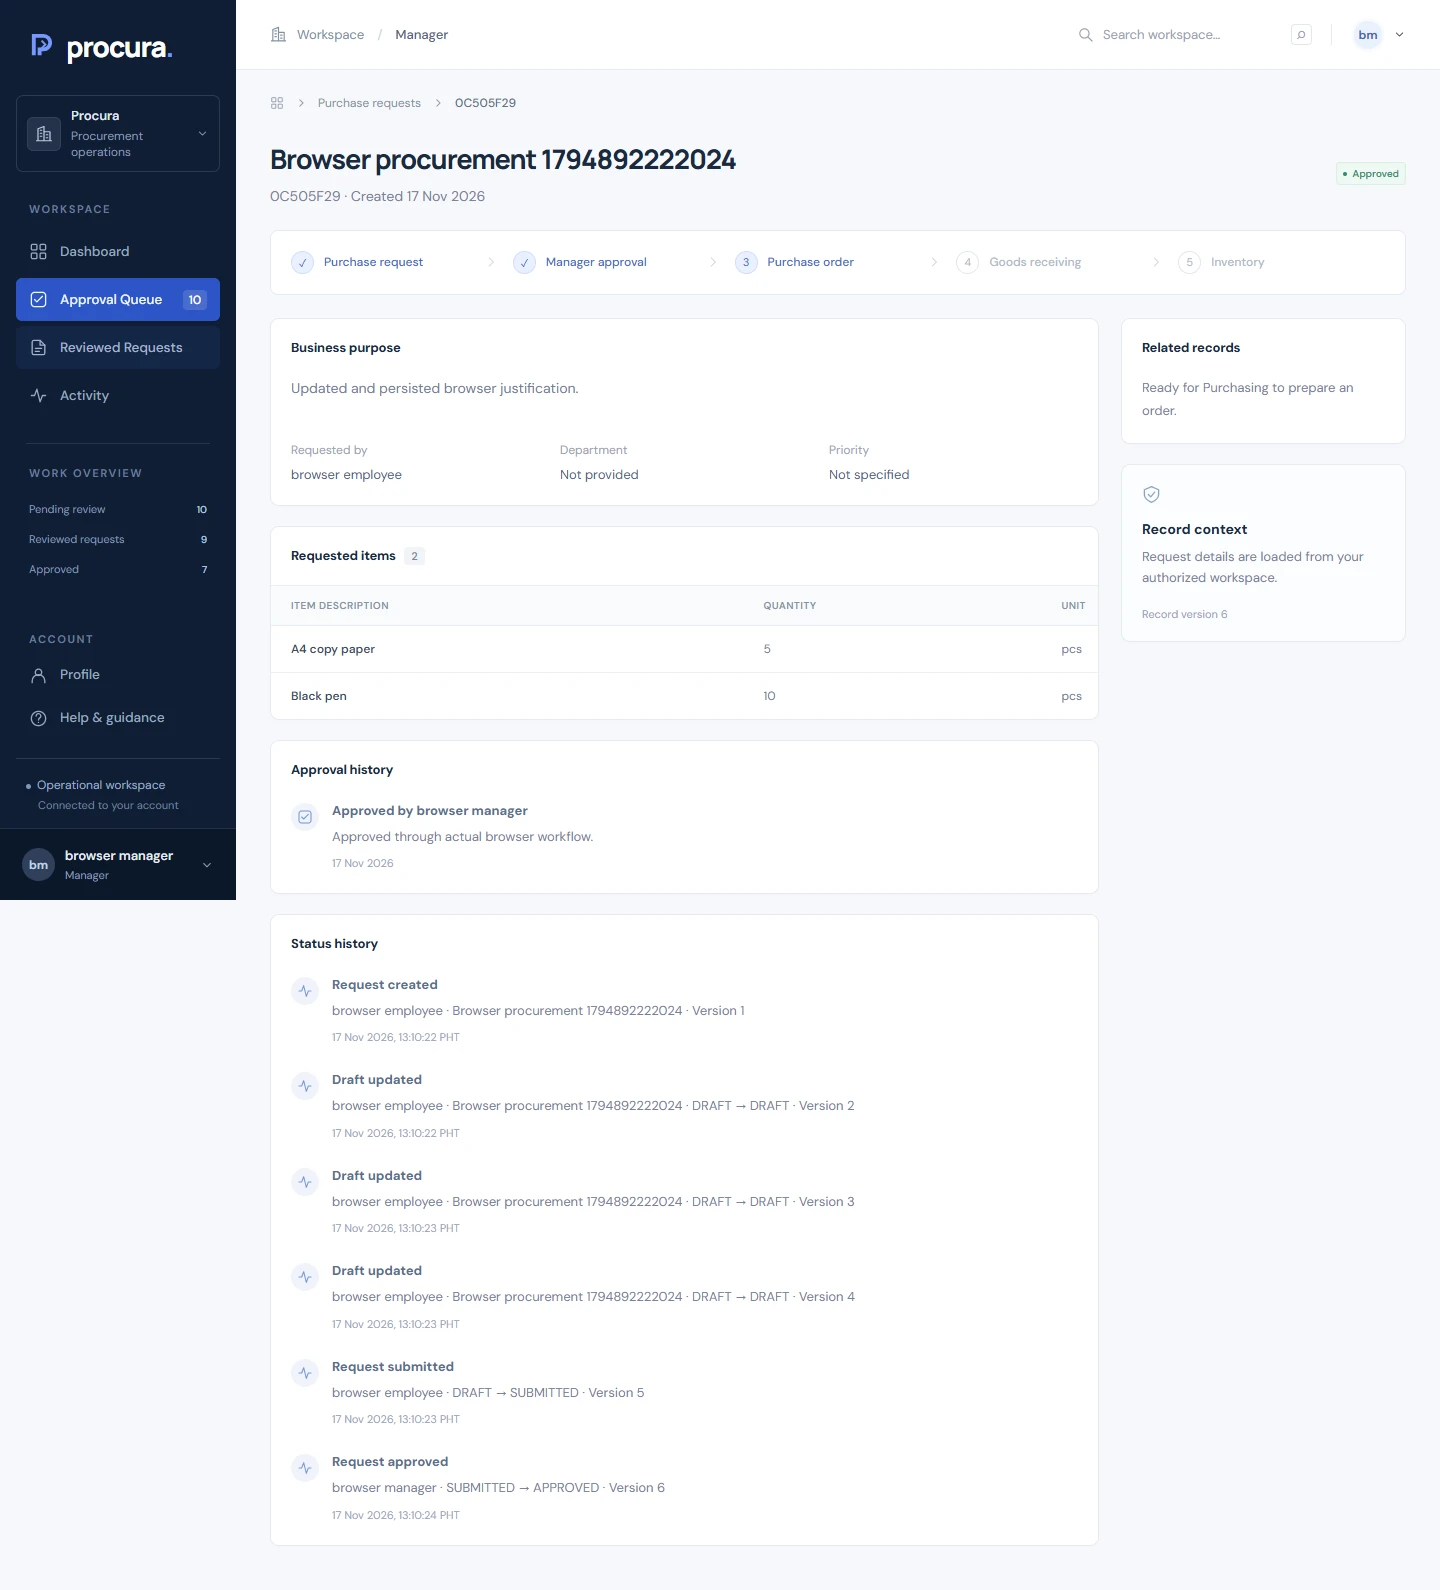
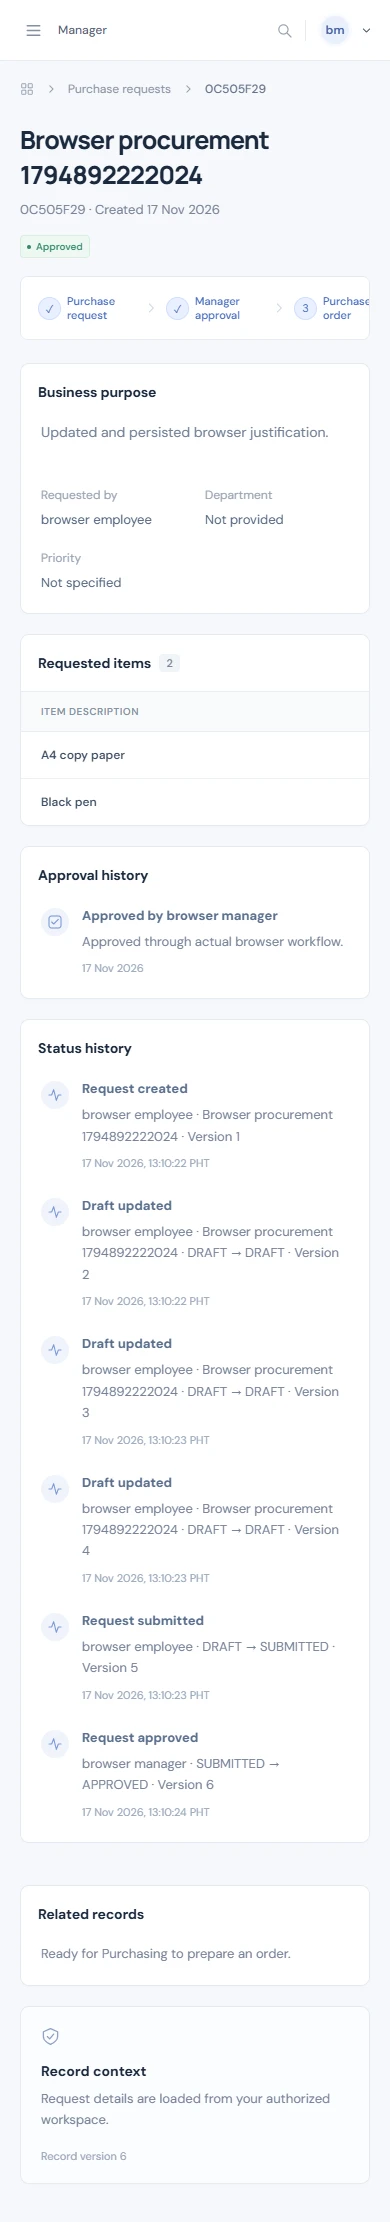
- PrepareCreate and edit owned drafts with validated line items.
- DecideManagers review submitted requests; self-approval and non-manager decisions are rejected.
- InspectSearch authorized records and inspect attributed status and approval history.
System architecture
React + Vite
Draft forms, review queue, server search and request history.
Express + Zod
Cookie sessions, object policies, validated commands and versions.
Prisma → PostgreSQL
Business write and audit event share one transaction.
- TypeScript
- React
- Express
- Prisma
- PostgreSQL
- Zod


Engineering decisions
Separate administration from approval
I keep approval as an explicit manager policy, with a self-approval check. An administrator can maintain an owned request without gaining decision authority.
Reviewed: Request policy and decision service
Reject stale decisions
Updates match the expected version and eligible state before changing anything. A stale edit or simultaneous decision returns a conflict instead of replacing newer work.
Reviewed: Version-aware request transactions
Implementation in focus
An approval without its audit event
- Problem
- If the request changes but history fails to save, a reviewer loses the explanation of who changed it.
- Implementation
- The decision, request version and audit insertion share a Prisma transaction. An audit-write failure rolls the business change back. Append-only controls protect ordinary event updates, not a privileged database owner.
Verification & status
Authorization, race & rollback test records
Local development report · 17 November 2026 · Uncommitted snapshot
The local report records 26 tests: 17 real PostgreSQL lifecycle tests and 9 unit/HTTP checks. Coverage includes simultaneous decisions, stale edits, self-approval denial and forced audit-failure rollback.
Reviewed 17 November results, not rerun here. This implementation is in an uncommitted local working tree ahead of the private GitHub baseline; no release or published-commit verification is claimed.
Request & approval slice
The request-to-approval workflow is persisted and connected to the interface. Captures show isolated database-backed browser tests.
Suppliers, orders, receiving, the inventory ledger and full reporting need persisted implementation. Dependency advisories and deployment/identity operations remain open.
Lessons & next steps
A workflow is only as trustworthy as its denied actions and failed writes. I treat conflict handling and audit rollback as product behavior, not just database details.
Review dependency advisories and stabilize the local milestone, then implement suppliers/orders before transaction-safe receiving.
Source & evidence access
The repository remains private. This case study shares reviewed implementation summaries and safe application captures, not source code or operational records.
Private local working tree based on cf40460, inspected 18 November 2026. Source remains private and unchanged by the portfolio work.